PARHAM · SOLUTIONS
Issues we solve, proof we produce.
Five disciplines, one workspace. Each solution below starts from the problem your team feels — and ends with the record your auditor wants. Features that power them all live on the Features page: one workbench, maker-checker, timed exceptions, dashboards, and local AI.
SOLUTION 01 / AUDIT & COMPLIANCE
Audits shouldn't start with a search party.
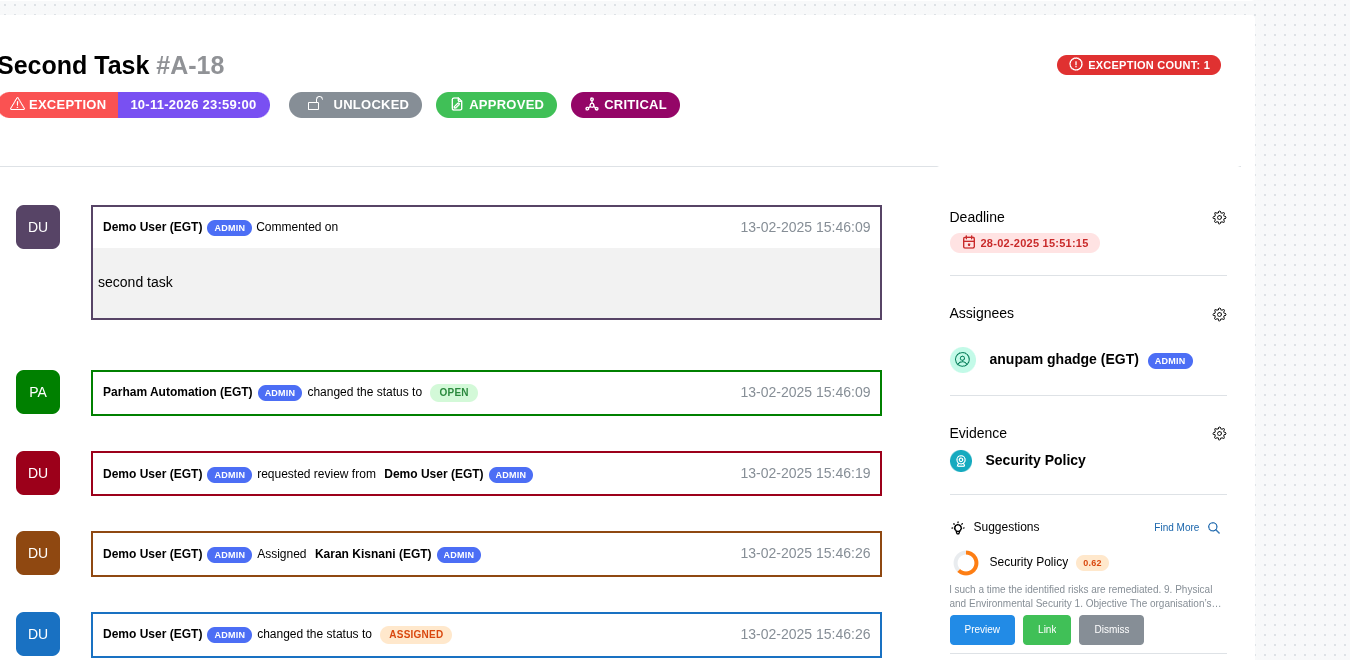
The audit cost isn't the finding — it's the six weeks of hunting for the evidence that closes it. Parham makes evidence a first-class citizen, attached to the finding it resolves, with the workflow to prove who did what, when.
- Audit issues as tracked work items — full lifecycle from open to closed, never a row in a spreadsheet that gets quietly deleted.
- Evidence attached to the finding — files and evidence records bound directly to each issue, not scattered across drives and inboxes.
- An evidence library that compounds — create evidence manually, or turn the artefacts and comments used to close any item — ticket, incident, risk, vulnerability — into reusable evidence records.
- Maker-checker by design — the person who closes is never the person who executed.
- Deadlines with teeth — due dates on every item, schedules and calendar views, overdue visible at a glance.
- A complete record — status history, comments, and organization-level audit logs.
- Dashboards and saved queries — the auditor's question answered in seconds, repeatedly, identically.
Local-AI advantage: evidence suggestions match each issue against your policies, circulars, and existing evidence — including artefacts that closed other items. Yesterday's proof resolves today's finding. Grounded answers carry citations.
SOLUTION 02 / STANDARDS
Assess once. Satisfy many.
ISO 27001. PCI DSS. RBI's cyber security framework. The standard your biggest customer invented. Most teams answer the same questions, for different auditors, in different spreadsheets. Parham runs them all on one framework-agnostic control engine — so a control assessed once produces evidence everywhere it's needed.
- A control engine, not a framework template — model any standard as criteria, controls, and checks.
- ISO 27001, curated in the box — every ISO 27001:2022 Annex A control, pre-mapped onto the unified control model.
- Regulators' frameworks, modelable — PCI DSS, RBI's cyber security framework, and other obligations model natively on the same engine.
- Cross-framework mapping — one control, many frameworks.
- Satisfaction workflow — compliant, partially compliant, non-compliant, or exempt, with versioned statements and next-review dates.
- Scoping that audits cleanly — out of scope with recorded justification.
- Library updates, reviewed — accept, disregard, or resolve manually. History stays yours.
SOLUTION 03 / ASSETS · IT/OT
One inventory for an estate that refuses to be one.
Servers and PLCs. Branch offices and substations. Parham gives you one asset registry flexible enough for all of it — and disciplined enough to audit.
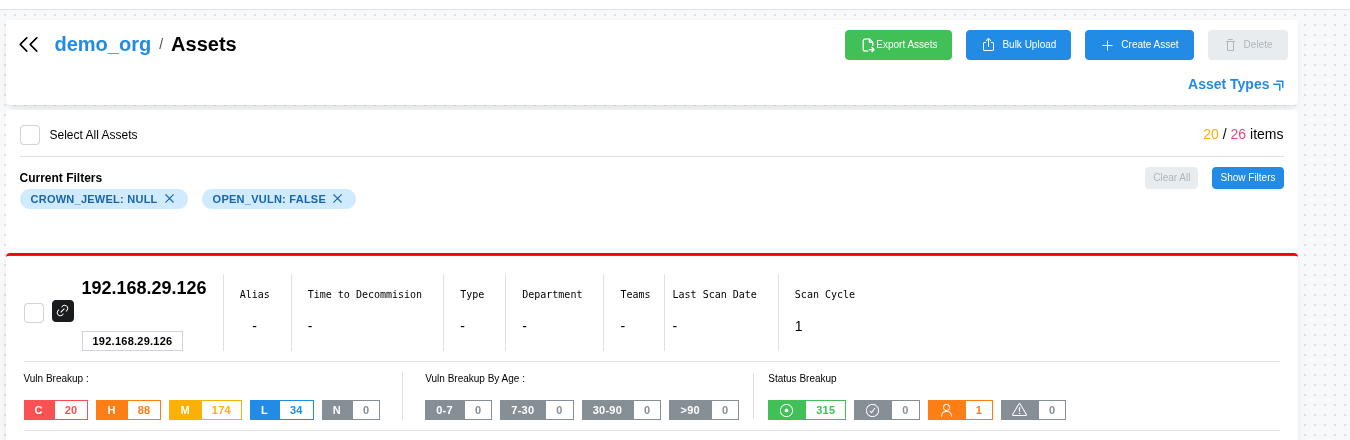
- A single asset registry — every host, display name, and alias in one place.
- Your taxonomy, not ours — custom asset types and tags for IT or OT.
- Crown-jewel designation — carries into vulnerability prioritization.
- Accountability by design — every asset owned by a department and team.
- Lifecycle discipline — decommission dates and liveness tracking.
- Vendor context per asset — linked procurement and support contacts.
- Risk that follows the asset — live risk score from most recent scans.
Building toward: native OT asset classes and OT-aware analytics.
SOLUTION 04 / THIRD-PARTY RISK
Know your third parties — without handing them your data.
The regulator made you responsible for your vendors. Parham puts your third-party estate in one register — and keeps it there.
- Complete vendor registry — vendors, contacts, contracts with PO numbers, terms, dates, statuses.
- Contracts connected to reality — asset-level linkage to procurement and support contacts.
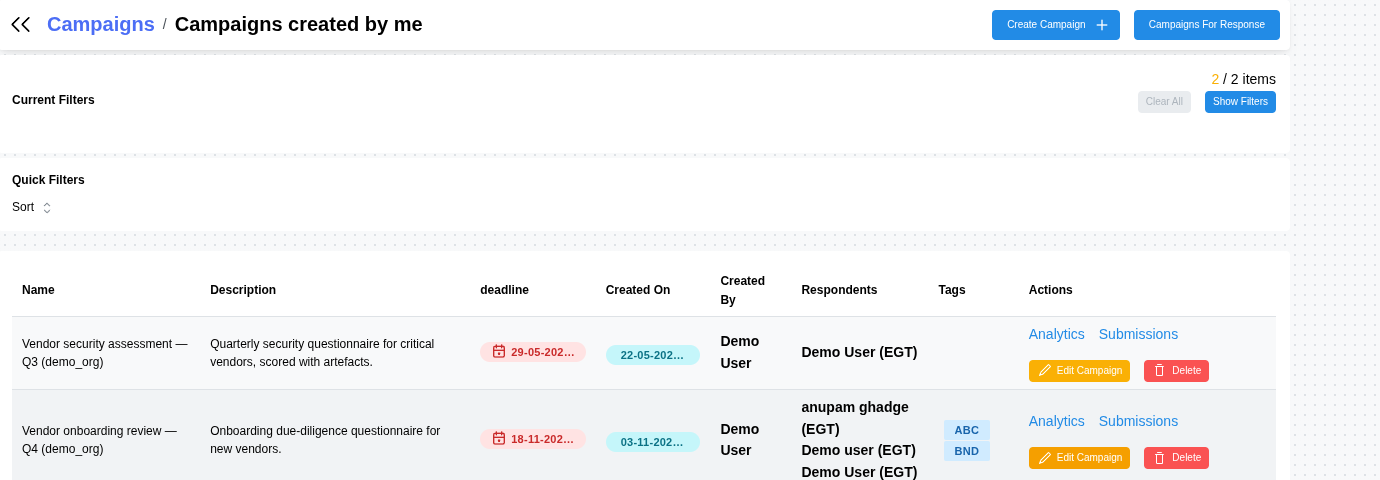
- Assessment campaigns — questionnaires, templates with grading, deadlines, including external respondents.
- Scored, evidenced responses — submissions with scores and artefacts reusable as evidence.
- Total recall — every vendor, contract, answer, and artefact queryable and time-stamped.
Building toward: vendor risk scoring and tiering.
SOLUTION 05 / VULNERABILITY MANAGEMENT
Your scanner finds them. Parham finishes them.
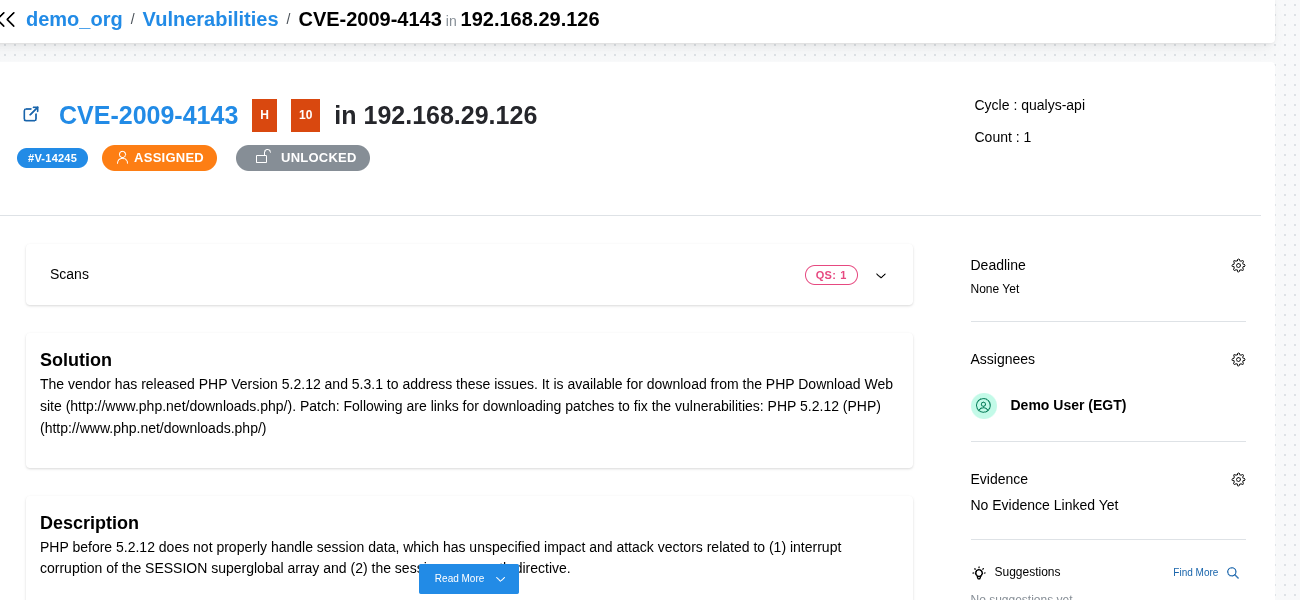
Scanning is solved. Closure isn't. Parham takes every scan result and turns it into an accountable work item — assigned, deadline-bound, reviewed, and closed with evidence.
- Multi-scanner ingestion — Nessus, Qualys, Tenable, and OpenVAS in one pipeline.
- Scan cycles with scope — defined asset set, coverage over time.
- CVE-to-asset instances — enriched with CVSS and CWE.
- Remediation with accountability — tickets linked to vulnerabilities, parent-child tracking.
- Exceptions that expire — formal risk acceptance with an end date.
- Closure that means something — maker-checker review before close.
Start where the pain is loudest.
Audit and standards today, vendors and vulnerabilities tomorrow — one workbench throughout. See how it works.